Stealth hacks don’t announce themselves with flashing alarms. You might not notice unusual traffic or hidden backdoors until your customers do—and by then, it’s too late. Continuous website threat monitoring lets you spot suspicious activity and detect unauthorized file changes before damage spreads. This guide walks you through how real time website monitoring and web application anomaly detection keep your defenses sharp with proactive cyber threat response.
Understanding the Hidden Nature of Modern Web Threats
The threat actors targeting your web infrastructure today operate with patience and precision. They establish footholds silently, move laterally through your systems without triggering traditional alerts, and exfiltrate data over weeks or months. Your conventional security tools may scan periodically, but attackers exploit the gaps between those scans to modify files, inject malicious code, and establish persistence mechanisms that survive reboots and updates.
This reality demands a fundamental shift in how you approach web security. Point-in-time security assessments create windows of vulnerability that sophisticated attackers exploit with ease. The modern threat landscape requires continuous website threat monitoring that provides uninterrupted visibility into every change, every request, and every anomaly across your web infrastructure.
The Cost of Detection Delay
When you detect unauthorized file changes days or weeks after the initial compromise, the damage compounds exponentially. Attackers use that time to map your network, identify valuable assets, establish multiple backdoors, and prepare for data extraction. The average dwell time for attackers in compromised systems extends beyond 200 days in many industries. Each day of undetected access increases your exposure to data breaches, regulatory penalties, and reputational damage that can take years to repair.
Your customers trust you to protect their data and maintain service availability. When a breach reaches public awareness, that trust evaporates rapidly. The organizations that maintain customer confidence are those that detect and respond to threats before they escalate into full-scale incidents.
The Foundation of Continuous Website Threat Monitoring
Effective continuous website threat monitoring builds on multiple layers of detection and response capabilities. Each layer addresses specific attack vectors while contributing to a comprehensive security posture that leaves attackers with no easy entry points.
File Integrity Monitoring at Scale
The ability to detect unauthorized file changes forms the cornerstone of web application security. Attackers frequently modify configuration files, inject malicious code into legitimate scripts, or plant web shells that provide persistent access. Traditional file integrity monitoring tools check files on scheduled intervals, creating gaps that attackers exploit.
Real time website monitoring examines file system changes as they occur. Modern file integrity systems use cryptographic hashing to create unique fingerprints for every file in your web application stack. When any file changes, the system immediately compares the new hash against the baseline and triggers alerts for unauthorized modifications.
This approach catches attacks at their earliest stages. When an attacker modifies a PHP file to include a backdoor, your monitoring system detects the change within seconds. You can investigate and remediate before the attacker leverages that backdoor for further exploitation.
Traffic Pattern Analysis
Web application anomaly detection extends beyond file monitoring to analyze request patterns, user behaviors, and data flows. Your web applications generate predictable traffic patterns under normal conditions. Requests follow expected sequences, users access resources in logical patterns, and data transfer volumes remain within established baselines.
Attackers disrupt these patterns. Reconnaissance activities generate unusual request sequences. Exploitation attempts trigger error responses at abnormal rates. Data exfiltration creates traffic spikes to unexpected destinations. Real time website monitoring systems establish behavioral baselines for your applications and alert you when traffic deviates from normal patterns.
Machine learning algorithms enhance this capability by adapting to legitimate changes in your application usage while maintaining sensitivity to malicious activity. The systems learn that traffic increases during business hours and decreases overnight. They recognize seasonal patterns and accommodate legitimate growth. They distinguish between a marketing campaign driving increased traffic and a distributed attack attempting to overwhelm your resources.
Authentication and Authorization Monitoring
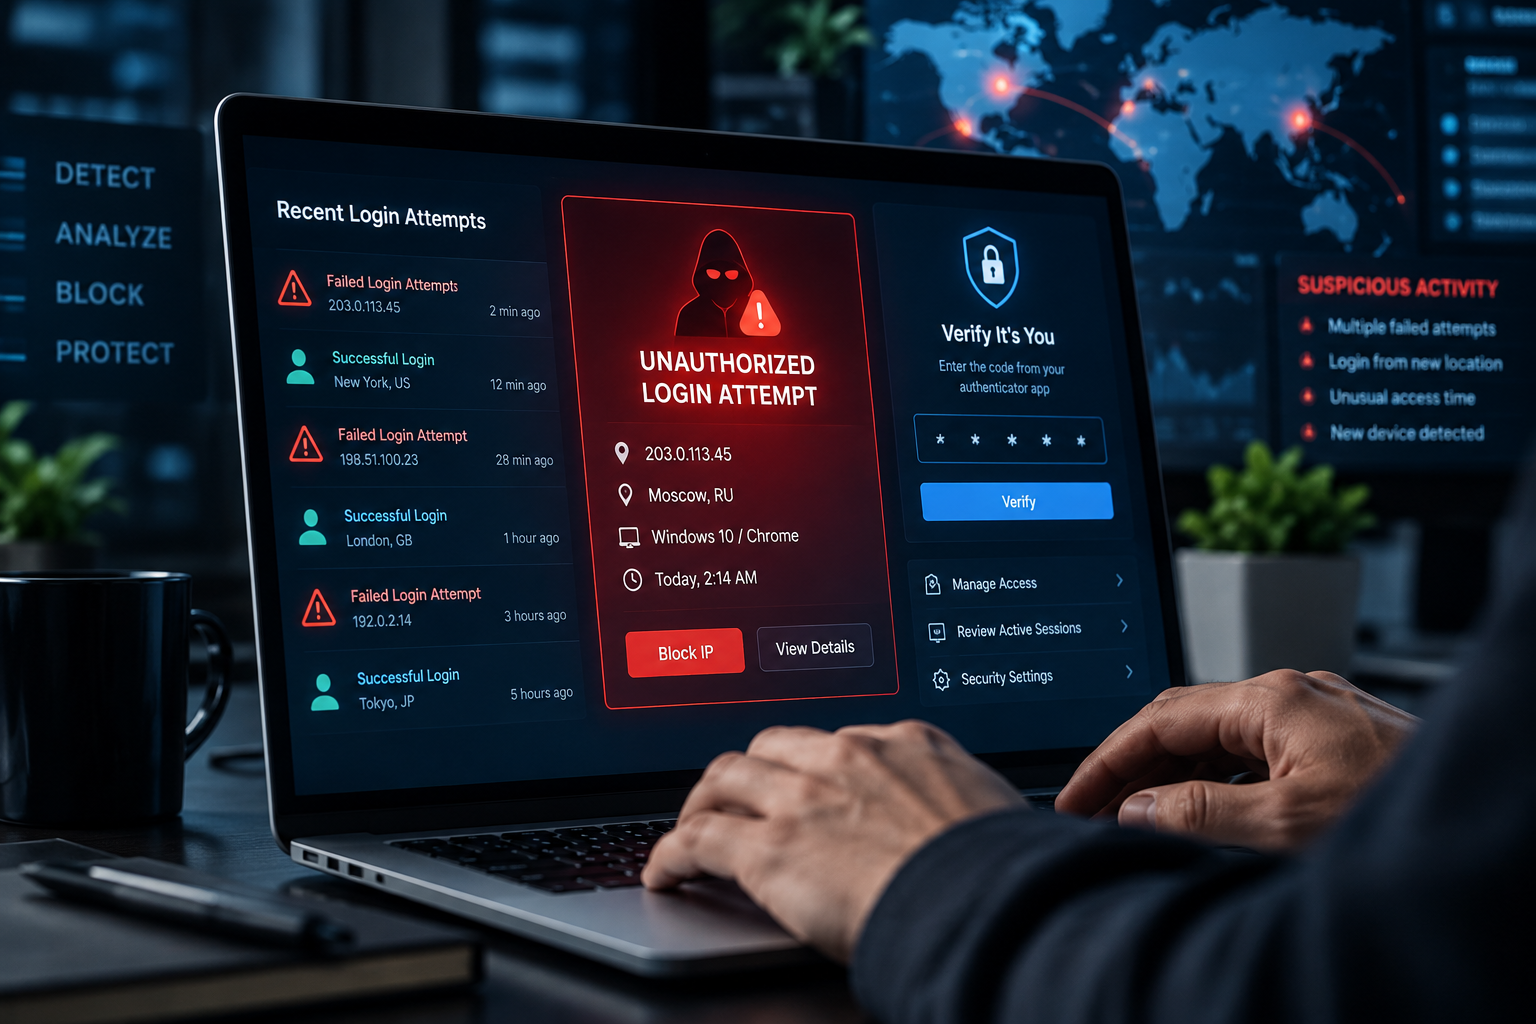
Attackers who gain initial access often attempt to escalate privileges or move laterally to more valuable systems. Continuous website threat monitoring tracks authentication attempts, privilege escalations, and access to sensitive resources. The systems flag failed login attempts from unusual locations, successful authentications outside normal business hours, and access to resources that specific users don’t typically need.
This layer of monitoring catches credential stuffing attacks, brute force attempts, and compromised account abuse. When an attacker uses stolen credentials to access your systems, the monitoring detects the anomalous behavior patterns that distinguish automated attacks from legitimate users.
Implementing Web Application Anomaly Detection
Effective web application anomaly detection requires careful planning and configuration. The systems must be sensitive enough to catch genuine threats while avoiding false positives that create alert fatigue and waste your security team’s time.
Establishing Accurate Baselines
Your monitoring systems need comprehensive baselines that represent normal operations. This process begins with a learning period during which the systems observe your applications under typical conditions. The systems catalog normal file states, document expected traffic patterns, and map legitimate user behaviors.
The baseline period should span sufficient time to capture variations in your business cycles. If your applications experience different load patterns on weekends, the baseline must include weekend data. If monthly reporting drives traffic spikes, the baseline should cover multiple month-end cycles.
During baseline establishment, ensure your systems are clean. If attackers have already compromised your environment, the baseline will incorporate malicious activity as normal behavior. Conduct thorough security assessments before implementing continuous website threat monitoring to verify you’re establishing baselines from a known-good state.
Tuning Detection Sensitivity
Once baselines exist, configure detection thresholds that balance sensitivity with practicality. Too sensitive, and your team drowns in false positives. Too permissive, and genuine attacks slip through undetected.
Start with conservative thresholds and adjust based on operational experience. Track which alerts represent genuine security events and which reflect legitimate but unusual activities. Refine your rules to reduce noise while maintaining detection capability.
Modern monitoring platforms support whitelist approaches that explicitly permit known-good activities. If your deployment process legitimately modifies files, create exceptions that allow those specific changes while still alerting on unexpected modifications. If legitimate users occasionally access your systems from new locations, implement risk-based authentication that requires additional verification rather than blocking access outright.
Integration with Incident Response Workflows
Detection without response provides limited value. Your continuous website threat monitoring systems must connect to incident response workflows that enable rapid investigation and remediation. When the system detects unauthorized file changes, your security team needs immediate access to context about the modification, affected systems, and potential impact.
Automated response capabilities enhance your security posture by containing threats before human analysts can intervene. When monitoring detects a web shell upload, automated systems can quarantine the affected server, block the attacker’s IP address, and preserve forensic evidence while alerting your security team.
This automation requires careful design to avoid disrupting legitimate operations. Implement graduated response procedures that match response intensity to threat severity. Low-confidence detections might generate alerts for human review. Medium-confidence detections could trigger enhanced logging and monitoring. High-confidence detections of known attack patterns justify immediate automated containment.
Building Proactive Cyber Threat Response Capabilities
The ultimate goal of continuous website threat monitoring extends beyond detection to enable proactive cyber threat response that stops attacks before they achieve their objectives. This requires moving from reactive incident handling to predictive threat hunting and preemptive defense.
Threat Intelligence Integration
Your monitoring systems become more effective when enriched with external threat intelligence. Global threat feeds provide information about emerging attack techniques, known malicious IP addresses, and indicators of compromise associated with active threat campaigns. Integrating this intelligence enables your systems to recognize attacks based on patterns observed across the broader security community.
When threat intelligence reports a new vulnerability being actively exploited, your monitoring can immediately increase scrutiny of requests targeting that vulnerability. When feeds identify IP addresses associated with attack infrastructure, your systems can block or flag traffic from those sources. This integration transforms your defenses from reactive to anticipatory.
Continuous Validation and Testing
Proactive cyber threat response requires ongoing validation that your defenses actually work as intended. Regular testing verifies that your continuous website threat monitoring detects the attacks you expect to face. Penetration testing and red team exercises simulate real attack scenarios to validate detection coverage and response procedures.
These exercises reveal gaps in your monitoring coverage. Perhaps certain file locations aren’t included in integrity monitoring. Maybe specific attack techniques don’t trigger alerts because they fall outside your detection rules. Testing identifies these weaknesses so you can address them before real attackers exploit them.
Automated attack simulation tools enable continuous validation without the cost and complexity of full-scale penetration tests. These tools execute known attack techniques against your systems in controlled ways, verifying that your monitoring detects each stage of the attack chain.
Metrics and Continuous Improvement
Effective security programs measure their performance and improve over time. Track key metrics that indicate the health of your continuous website threat monitoring program. Mean time to detect measures how quickly you identify security incidents. Mean time to respond tracks how long remediation takes. False positive rates indicate whether your tuning efforts are successful.
Analyze trends in these metrics to identify improvement opportunities. If detection times increase, investigate whether changes in your environment have created new blind spots. If response times grow, examine whether your incident response procedures need streamlining or your team needs additional resources.
Regular reviews of detected incidents provide learning opportunities. For each security event, conduct post-incident analysis to understand how the attack succeeded, why detection occurred when it did, and what could have enabled earlier detection. Apply these lessons to refine your monitoring rules and detection logic.
Selecting the Right Monitoring Tools and Technologies
The market offers numerous solutions for continuous website threat monitoring, each with different capabilities and approaches. Selecting the right tools requires understanding your specific requirements and evaluating solutions against those needs.
Core Capability Requirements
Your monitoring solution must provide real time website monitoring across all components of your web infrastructure. This includes web servers, application servers, databases, and any supporting systems that contribute to your web presence. The solution should detect unauthorized file changes across all monitored systems with minimal latency between modification and detection.
Web application anomaly detection capabilities should extend beyond simple signature-based detection to include behavioral analysis that identifies novel attacks. The system should establish baselines automatically and adapt to legitimate changes in your environment without manual reconfiguration.
Look for solutions that provide centralized visibility across distributed environments. If your web infrastructure spans multiple data centers or cloud providers, your monitoring must aggregate data from all locations into unified dashboards and alert streams. Security teams cannot effectively respond to threats when critical information is scattered across multiple disconnected tools.
Scalability and Performance Considerations
Your monitoring solution must operate at the scale of your infrastructure without degrading application performance. File integrity monitoring that scans millions of files should complete quickly enough to detect changes in near real time. Traffic analysis must process high-volume request streams without introducing latency that affects user experience.
Evaluate solutions under load conditions that match your production environment. Vendors often demonstrate capabilities using small test deployments that don’t reflect the complexity and scale of enterprise web infrastructures. Request proof-of-concept deployments in your environment to verify performance at scale.
Consider future growth in your evaluation. Your web infrastructure will expand as your business grows. The monitoring solution you select today must scale to accommodate that growth without requiring complete replacement.
Integration and Ecosystem Compatibility
Modern security operations rely on integrated tool chains that share data and coordinate responses. Your continuous website threat monitoring solution should integrate with your security information and event management (SIEM) platform, threat intelligence feeds, incident response tools, and IT service management systems.
API availability and quality determine integration success. Evaluate the comprehensiveness of each vendor’s API offerings. Can you extract all relevant data programmatically? Can you configure detection rules through the API? Does the API support automation of response actions?
Consider the vendor’s ecosystem and partnership network. Solutions with broad integration support reduce the custom development required to connect your security tools. Established vendors typically offer pre-built integrations with common security platforms.
Overcoming Implementation Challenges
Organizations implementing continuous website threat monitoring encounter common challenges that can derail deployments if not addressed proactively. Understanding these challenges and planning mitigation strategies ensures successful implementation.
Managing Alert Volume
The transition from periodic scanning to continuous monitoring often produces dramatic increases in alert volume. Systems that previously checked files daily now detect every change as it occurs. This flood of alerts can overwhelm security teams if not managed carefully.
Address this challenge through careful tuning and prioritization. Not all detected changes represent security incidents. Legitimate application updates, configuration changes, and routine maintenance activities generate alerts that require acknowledgment but not investigation. Configure your systems to distinguish between expected changes and suspicious modifications.
Implement alert prioritization that focuses analyst attention on the highest-risk events. Changes to critical system files warrant immediate investigation. Modifications to static content files may require only acknowledgment. Traffic anomalies from known-malicious sources demand urgent response. Unusual but benign traffic patterns might generate informational alerts for trending analysis.
Balancing Security and Operations
Continuous website threat monitoring introduces new processes and controls that can conflict with existing operational procedures. Development teams accustomed to deploying changes directly to production may resist file integrity monitoring that flags their updates. Operations teams may push back against traffic analysis that questions routine administrative activities.
Successful implementation requires collaboration between security and operational teams. Involve operations staff in baseline definition and tuning processes. Ensure monitoring systems accommodate legitimate operational activities through appropriate exceptions and change management integration.
Create clear escalation procedures that define when security concerns override operational convenience. Critical security alerts may justify blocking deployments or restricting access. Lower-severity findings might be logged and reviewed without disrupting operations.
Resource and Skill Requirements
Effective continuous website threat monitoring requires skilled security analysts who understand web application architecture, attack techniques, and incident response procedures. Many organizations struggle to staff security teams with appropriate expertise.
Address skill gaps through training, automation, and managed services. Invest in training programs that build your team’s capabilities in web security and threat detection. Implement automation that handles routine analysis and response tasks, freeing skilled analysts to focus on complex investigations. Consider managed security services that supplement your internal team with external expertise.
The Strategic Value of Proactive Cyber Threat Response
Organizations that implement effective continuous website threat monitoring gain strategic advantages beyond improved security. These capabilities enable business initiatives that would be too risky without comprehensive visibility and rapid response.
Enabling Digital Transformation
Digital transformation initiatives often introduce new attack surfaces and security risks. Moving applications to cloud platforms, exposing APIs to partners, and implementing customer-facing portals all expand the scope of potential compromise. Continuous website threat monitoring provides the visibility and control needed to pursue these initiatives confidently.
With real time website monitoring, you can detect and respond to attacks against new digital services before they impact customers or compromise sensitive data. This capability removes security concerns as blockers to digital innovation.
Supporting Compliance Requirements
Regulatory frameworks increasingly mandate continuous monitoring and rapid incident response. Standards like PCI DSS require file integrity monitoring for payment systems. GDPR mandates timely breach notification. HIPAA requires security incident detection and response capabilities.
Comprehensive continuous website threat monitoring provides the evidence needed to demonstrate compliance. Detailed logs of file changes, traffic patterns, and security events support audit requirements. Documented detection and response times prove you meet regulatory standards for incident handling.
Protecting Brand Reputation
Your web presence represents your brand to customers and partners. Website defacement, service disruptions, and data breaches damage reputation in ways that take years to repair. The ability to detect unauthorized file changes and respond before attacks become public incidents protects the brand equity you’ve built.
Customers increasingly expect the organizations they trust with their data to maintain strong security. Public demonstrations of security competence through rapid threat detection and response build customer confidence. Conversely, high-profile breaches that could have been prevented through better monitoring erode trust permanently.
Moving Forward with Confidence
The threat landscape facing your web infrastructure will continue to grow more complex and challenging. Attackers develop new techniques, exploit emerging vulnerabilities, and target the gaps in your defenses. Staying ahead of these threats requires continuous website threat monitoring that provides complete visibility and enables proactive cyber threat response.
The investment in comprehensive monitoring capabilities pays dividends through reduced breach risk, faster incident response, and the confidence to pursue digital initiatives that drive business growth. Organizations that detect unauthorized file changes within seconds rather than days limit damage and maintain customer trust. Those that leverage web application anomaly detection catch attacks that signature-based tools miss entirely.
Your path forward begins with honest assessment of your current capabilities. Evaluate whether your existing tools provide truly continuous monitoring or merely periodic scanning. Determine whether you can detect unauthorized file changes in real time or only during scheduled scans. Assess whether your traffic analysis catches novel attacks or only known signatures.
Based on this assessment, develop a roadmap for enhancing your monitoring capabilities. Prioritize gaps that represent the highest risk to your organization. Implement solutions that address those gaps while building toward comprehensive coverage.
The organizations that thrive in today’s threat environment are those that shift from reactive incident response to proactive threat hunting. They detect attacks early, respond rapidly, and continuously improve their defenses. With the right approach to continuous website threat monitoring, your organization can join their ranks and face the future with confidence.
Frequently Asked Questions
What is continuous website threat monitoring and how does it differ from traditional security scanning?
Continuous website threat monitoring provides real-time, uninterrupted visibility into your web infrastructure, detecting threats as they occur rather than during scheduled scans. Traditional security tools check systems periodically, creating windows of vulnerability between scans that attackers exploit. Continuous monitoring examines file changes, traffic patterns, and access attempts instantly, catching attacks within seconds rather than hours or days.
How can I detect unauthorized file changes before they impact my customers?
Implement file integrity monitoring that uses cryptographic hashing to create unique fingerprints for every file in your web application stack. When any file changes, the system immediately compares the new hash against the baseline and triggers alerts for unauthorized modifications. This approach catches backdoors, malicious code injections, and configuration tampering at the earliest stages, often before attackers can leverage those changes.
What types of traffic anomalies indicate a potential security breach?
Suspicious traffic patterns include unusual request sequences from reconnaissance activities, abnormal error response rates from exploitation attempts, traffic spikes to unexpected destinations indicating data exfiltration, failed login attempts from unusual locations, and successful authentications outside normal business hours. Web application anomaly detection systems establish behavioral baselines for your applications and alert you when traffic deviates significantly from normal patterns.
How quickly should I be able to detect and respond to web application threats?
Best-in-class organizations detect security incidents within minutes of occurrence and begin response procedures within 15 to 30 minutes. Real time website monitoring enables detection in seconds for file modifications and within minutes for traffic anomalies. Your mean time to detect should be measured in minutes, not hours or days, while mean time to respond should allow containment before attackers can move laterally or exfiltrate significant data.
What resources do I need to implement effective continuous website threat monitoring?
You need monitoring tools that provide real-time file integrity checking and traffic analysis, skilled security analysts who understand web application architecture and attack techniques, integration with your incident response workflows and SIEM platform, and sufficient compute resources to analyze traffic without degrading application performance. Many organizations supplement internal teams with managed security services to address skill gaps and provide 24/7 monitoring coverage.
How Elevated Marketing can help
We do this work every day for businesses in Indianapolis, the DC & Virginia metro, and nationwide.
→ Website Security & Monitoring→ SEO & GEO Services→ Managed Web Hosting→ More on UncategorizedGet a free audit