Data breaches don’t just happen—they spiral fast, often within minutes. You need a website security incident response that stops threats before they snowball. With proactive web anomaly monitoring, your team can catch breaches inside 15 minutes, keeping your business running without a hitch.
Understanding the Critical 15-Minute Window
Why Speed Matters in Incident Response
When a security breach occurs, the first 15 minutes determine whether you contain a minor incident or face a full-scale crisis. Research shows that attackers move rapidly once they gain access to systems, exfiltrating data, installing backdoors, and escalating privileges at alarming speeds. For Operations Officers and Risk Managers at mid-market firms, this reality creates an urgent need for website security incident response capabilities that operate faster than traditional methods allow.
The financial impact of delayed detection grows exponentially with time. Every minute that passes allows attackers to penetrate deeper into your infrastructure, access more sensitive data, and create additional entry points for future attacks. Mid-market companies face particular vulnerability because they often lack the extensive security teams that enterprise organizations maintain, yet they hold valuable data that makes them attractive targets.
The Cost of Reactive Security Postures
Traditional security approaches that rely on periodic scans and manual reviews leave dangerous gaps in protection. By the time quarterly audits or monthly security reviews detect anomalies, attackers have already achieved their objectives. The average time to detect a breach in organizations using reactive methods exceeds 200 days, according to industry research. This extended exposure period allows criminals to thoroughly compromise systems, steal intellectual property, and establish persistent access mechanisms.
Mid-market firms cannot afford this level of risk. Your operations depend on maintaining customer trust, protecting proprietary information, and ensuring regulatory compliance. A single prolonged breach can result in regulatory fines, customer churn, and reputational damage that takes years to repair. The solution lies in shifting from reactive security measures to proactive web anomaly monitoring that identifies threats as they emerge.
Core Components of Proactive Web Anomaly Monitoring
Real-Time Traffic Analysis
Proactive web anomaly monitoring begins with continuous analysis of all traffic flowing to and from your web properties. This system establishes baseline patterns of normal behavior, then flags deviations that indicate potential security threats. Unlike traditional signature-based detection that only catches known attack patterns, behavioral analysis identifies zero-day exploits and novel attack methods by recognizing abnormal activity.
The monitoring system tracks multiple dimensions of web traffic simultaneously. It examines request volumes, geographic origins, user agent strings, request patterns, and payload characteristics. When traffic exhibits characteristics inconsistent with established baselines, the system generates immediate alerts that trigger your website security incident response protocols.
For Risk Managers concerned about false positives, modern proactive web anomaly monitoring employs machine learning algorithms that continuously refine their understanding of legitimate traffic patterns. This adaptive approach reduces alert fatigue while maintaining high sensitivity to genuine threats. Your security team receives actionable intelligence rather than overwhelming volumes of low-quality alerts.
Automated Website File Integrity Monitoring
Attackers who successfully breach web applications often modify files to maintain persistence, create backdoors, or alter functionality. Automated website file integrity monitoring provides a critical defense layer by detecting unauthorized changes to your web assets within minutes of occurrence.
This monitoring approach creates cryptographic hashes of all legitimate files in your web environment. The system continuously compares current file states against these baseline hashes, immediately flagging any modifications. When an attacker injects malicious code into a PHP file, adds a backdoor script, or modifies configuration files, the automated website file integrity monitoring system detects the change and triggers alerts before the compromised files can cause damage.
The automation aspect proves critical for mid-market firms with limited security staff. Manual file integrity checks require substantial time and expertise, making frequent verification impractical. Automated systems perform these checks continuously without human intervention, providing constant protection without increasing operational overhead.
Brute Force Login Protection
Credential-based attacks represent one of the most common breach vectors targeting mid-market organizations. Attackers use automated tools to attempt thousands of username and password combinations, seeking to compromise legitimate accounts. Brute force login protection mechanisms detect and block these attacks before they succeed.
Advanced brute force login protection goes beyond simple rate limiting. The system analyzes login attempt patterns, identifying distributed attacks that spread attempts across multiple IP addresses to evade basic defenses. It recognizes credential stuffing attacks that use previously breached credentials from other services. The protection mechanisms also detect anomalous login behaviors, such as access attempts from unusual geographic locations or at atypical times.
When the system identifies brute force activity, it implements graduated response measures. Initial detection triggers enhanced authentication requirements, such as multi-factor verification. Continued attack activity results in temporary account locks and IP address blocking. Throughout this process, your security team receives detailed reporting on attack characteristics, enabling informed decisions about additional protective measures.
Building a 15-Minute Incident Response Capability
Detection and Alert Generation
The foundation of rapid website security incident response lies in immediate threat detection. Proactive web anomaly monitoring systems generate alerts within seconds of identifying suspicious activity. These alerts include comprehensive context about the detected anomaly, including affected systems, attack vectors, traffic sources, and potential impact.
For Operations Officers managing multiple business priorities, alert quality matters as much as speed. The monitoring system prioritizes alerts based on threat severity and potential business impact. Critical threats that could immediately compromise sensitive data or disrupt operations receive highest priority, while lower-risk anomalies are categorized for review during normal security operations.
The alert system integrates with your existing communication infrastructure, delivering notifications through multiple channels. Email, SMS, and integration with incident management platforms ensure that appropriate personnel receive threat information regardless of their location or current activities. This multi-channel approach supports the rapid mobilization required for effective incident response.
Automated Initial Response Actions
While human judgment remains essential for complex security decisions, automated response capabilities handle routine threat mitigation tasks instantly. When proactive web anomaly monitoring detects common attack patterns, the system can execute predefined response actions without waiting for human intervention.
Automated responses include blocking malicious IP addresses, isolating compromised accounts, disabling suspicious file uploads, and activating enhanced logging for affected systems. These immediate actions contain threats while your security team assesses the situation and determines appropriate next steps. The automation ensures consistent, rapid response even during off-hours when security staff may not be immediately available.
For Risk Managers concerned about automation errors, modern systems include safeguards that prevent automated responses from disrupting legitimate business operations. The response logic incorporates confidence thresholds, ensuring that only high-certainty threats trigger blocking actions. Lower-confidence detections generate alerts for human review rather than executing automated blocks.
Coordinated Human Response
After automated systems contain the immediate threat, your security team executes detailed investigation and remediation activities. The proactive web anomaly monitoring system provides comprehensive forensic data that accelerates this investigation phase. Detailed logs show exactly what the attacker accessed, what actions they attempted, and what changes they made to your systems.
This forensic information enables your team to assess the full scope of the incident within the critical 15-minute window. You can determine whether the attack represents an isolated probe or part of a broader campaign. The data reveals whether attackers accessed sensitive information, requiring customer notifications and regulatory disclosures. Armed with this intelligence, you make informed decisions about escalation, containment, and recovery actions.
The system also supports transparent English-language reporting that communicates incident details to non-technical stakeholders. Operations Officers can quickly understand what happened, what risks emerged, and what actions the security team is taking. This transparency supports informed business decisions about customer communications, regulatory notifications, and operational adjustments.
Web Threat Mitigation Strategies
Layered Defense Architecture
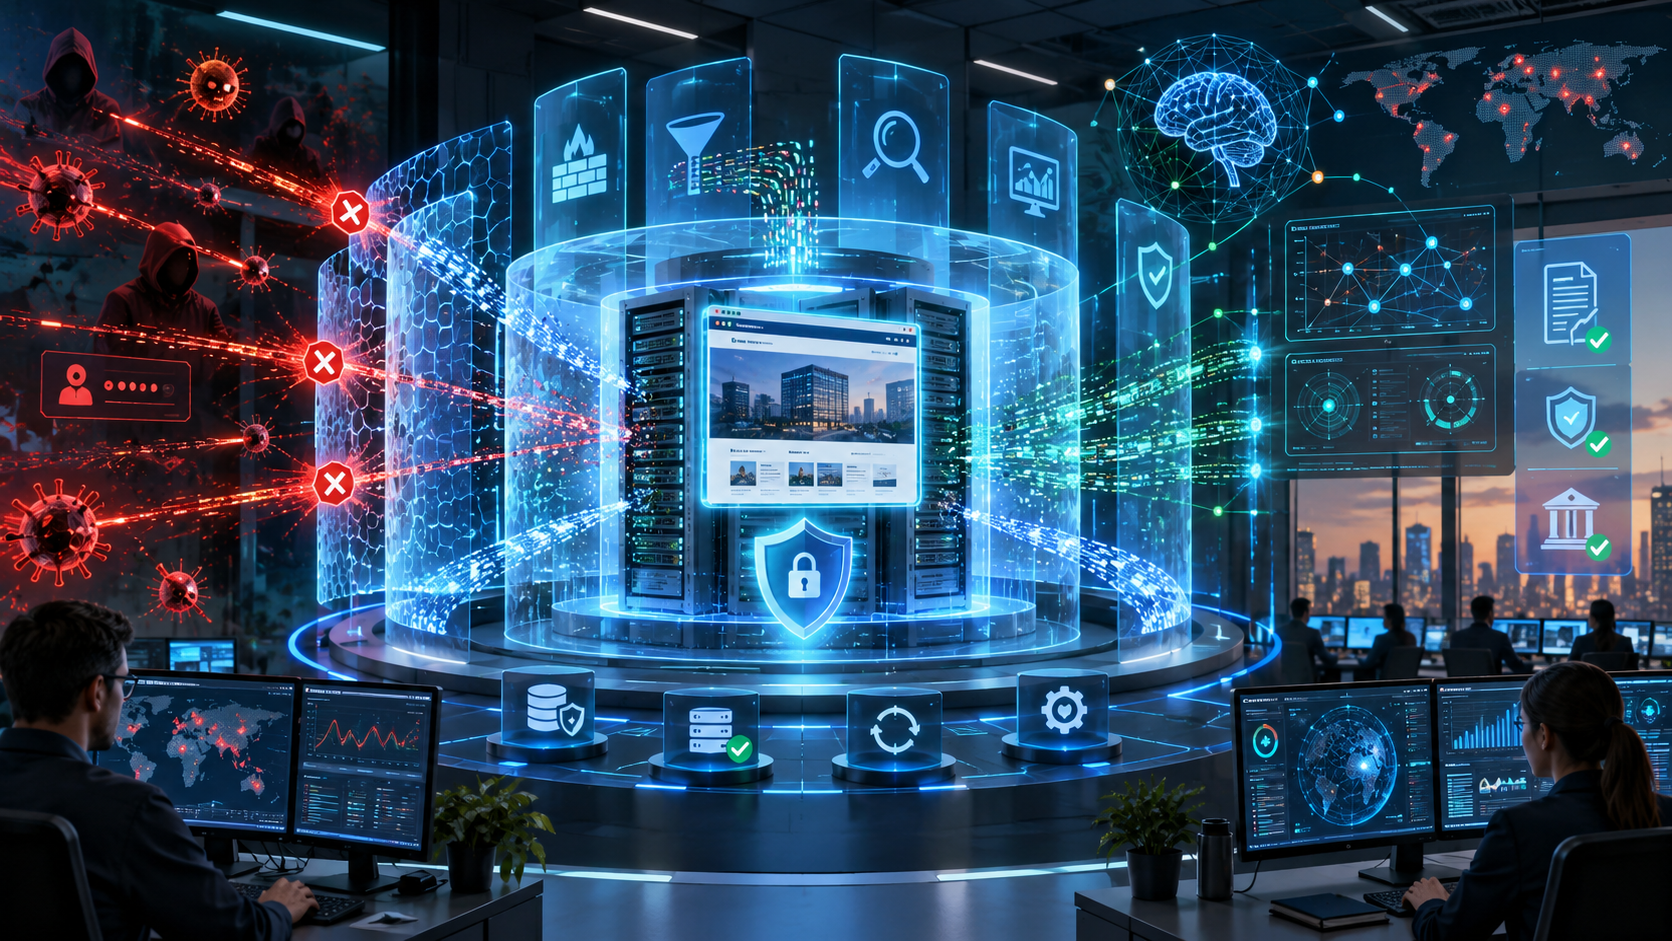
Effective web threat mitigation requires multiple defensive layers working in concert. Proactive web anomaly monitoring serves as a critical detection layer, but comprehensive protection includes preventive controls, detection mechanisms, and response capabilities.
Preventive controls include web application firewalls, input validation, secure coding practices, and regular security patching. These measures block common attack vectors before they reach your applications. Detection mechanisms like proactive web anomaly monitoring and automated website file integrity monitoring identify threats that bypass preventive controls. Response capabilities enable rapid containment and remediation when attacks occur.
This layered approach ensures that no single point of failure can compromise your entire security posture. If attackers bypass one defensive layer, additional controls detect and block their activities. For mid-market firms with resource constraints, this architecture provides enterprise-grade protection without requiring proportional security staff increases.
Continuous Improvement Through Threat Intelligence
Web threat mitigation improves over time as systems learn from detected attacks and incorporate external threat intelligence. Each incident provides data about attacker tactics, techniques, and procedures. The proactive web anomaly monitoring system uses this information to refine its detection algorithms, improving accuracy and reducing response times for future incidents.
External threat intelligence feeds provide information about emerging attack methods, compromised credential databases, and malicious infrastructure. Integration of this intelligence enhances your defensive capabilities by enabling preemptive blocking of known threat sources and early detection of new attack patterns targeting your industry.
For Risk Managers responsible for maintaining appropriate security investments, this continuous improvement model provides growing value over time. The initial deployment establishes baseline protection, while ongoing learning and intelligence integration progressively strengthen your security posture without proportional cost increases.
Compliance and Regulatory Alignment
Many mid-market firms operate under regulatory frameworks that mandate specific security controls and incident response capabilities. Proactive web anomaly monitoring supports compliance with requirements from standards like PCI DSS, HIPAA, GDPR, and SOC 2.
The detailed logging and reporting capabilities provide evidence of security control effectiveness during audits. Automated website file integrity monitoring satisfies requirements for change detection and configuration management. Brute force login protection demonstrates implementation of access control safeguards. The comprehensive documentation generated by these systems simplifies compliance reporting and reduces audit preparation time.
The 15-minute incident response capability directly addresses regulatory requirements for timely breach detection and notification. Many frameworks specify maximum timeframes for identifying and reporting security incidents. Proactive monitoring ensures you meet these obligations while protecting your organization from the business consequences of prolonged breaches.
Implementation Considerations for Mid-Market Firms
Resource Allocation and Staffing
Mid-market organizations must balance security investments against other business priorities. Proactive web anomaly monitoring provides substantial security improvements without requiring large security team expansions. The automated detection and response capabilities enable small security teams to achieve protection levels previously available only to organizations with extensive security operations centers.
When planning implementation, consider the skills required for system management and incident response. While automation handles routine tasks, your team needs expertise in security analysis, forensic investigation, and incident coordination. Many mid-market firms address this requirement through managed security service providers who supplement internal capabilities with specialized expertise.
The transparent reporting capabilities of modern systems also reduce the technical knowledge required for executive oversight. Operations Officers and Risk Managers can monitor security posture and incident trends without deep technical expertise, enabling informed governance without extensive security training.
Integration with Existing Infrastructure
Successful deployment requires integration with your existing technology environment. Proactive web anomaly monitoring systems connect with web servers, application platforms, databases, and network infrastructure. The implementation process should minimize disruption to ongoing operations while establishing comprehensive monitoring coverage.
Modern monitoring platforms support flexible deployment models that adapt to diverse infrastructure configurations. Whether you operate on-premises data centers, cloud environments, or hybrid architectures, the monitoring system can provide consistent protection across all components. API-based integration enables connection with your existing security tools, creating a unified security ecosystem rather than isolated point solutions.
For organizations concerned about implementation timelines, phased deployment approaches allow progressive expansion of monitoring coverage. Initial deployment might focus on the most critical web applications and customer-facing systems, with subsequent phases extending coverage to additional assets. This approach provides immediate protection for high-value targets while spreading implementation effort over manageable timeframes.
Measuring Success and ROI
Quantifying the value of proactive web anomaly monitoring helps justify ongoing investments and guide resource allocation decisions. Key metrics include mean time to detection, mean time to containment, number of incidents prevented, and reduction in successful breaches compared to historical baselines.
Financial metrics translate security improvements into business terms. Calculate the cost of breaches prevented by multiplying the number of blocked attacks by average breach costs in your industry. Compare this value against the cost of the monitoring system to demonstrate return on investment. Include indirect benefits like reduced regulatory risk, improved customer trust, and decreased insurance premiums in your analysis.
For Risk Managers reporting to executive leadership, these metrics support data-driven conversations about security investments. Rather than justifying security spending based on fear or compliance requirements, you present concrete evidence of business value delivered through proactive threat detection and rapid incident response.
The Strategic Advantage of Proactive Security
Organizations that implement proactive web anomaly monitoring gain strategic advantages beyond immediate threat protection. The ability to detect and contain security incidents within 15 minutes becomes a competitive differentiator in markets where customers increasingly prioritize data protection and privacy.
Your website security incident response capabilities directly impact customer trust and retention. When prospects evaluate potential vendors, they assess security practices as part of their due diligence process. Demonstrating advanced monitoring and rapid response capabilities positions your organization as a trustworthy partner that takes data protection seriously.
The operational stability enabled by effective web threat mitigation supports business growth and expansion. You can pursue new markets, develop additional digital services, and increase online transaction volumes with confidence that your security infrastructure will protect these initiatives. This security foundation removes barriers to digital transformation that might otherwise constrain business development.
For mid-market firms competing against larger enterprises, proactive security capabilities help level the playing field. Customers receive protection comparable to what major corporations provide, but with the responsiveness and personal attention that mid-market organizations deliver. This combination of enterprise-grade security and mid-market service quality creates compelling value propositions.
Moving Forward with Confidence
The threat environment facing mid-market organizations continues to grow more sophisticated and aggressive. Attackers recognize that these firms often hold valuable data while maintaining less extensive security programs than large enterprises. This combination makes mid-market companies attractive targets that require strong defensive capabilities.
Proactive web anomaly monitoring provides the detection speed and response capabilities necessary to protect your organization in this challenging environment. The 15-minute incident response window transforms security from a reactive cost center into a proactive business enabler. You gain the confidence to pursue digital initiatives, expand online operations, and compete effectively in increasingly digital markets.
The investment in automated website file integrity monitoring, brute force login protection, and comprehensive web threat mitigation delivers measurable returns through prevented breaches, maintained business continuity, and enhanced competitive positioning. For Operations Officers and Risk Managers responsible for protecting organizational assets while enabling business growth, these capabilities provide essential tools for achieving both objectives simultaneously.
Your path forward begins with assessing your current security posture and identifying gaps between existing capabilities and the protection requirements your business faces. Engage with security experts who understand mid-market constraints and opportunities. Develop an implementation roadmap that establishes proactive monitoring capabilities while respecting budget realities and resource limitations.
The organizations that thrive in coming years will be those that recognize security as a business enabler rather than a technical obligation. Proactive web anomaly monitoring represents a foundational capability for this strategic approach to security, providing the visibility, speed, and control necessary for confident business operations in an uncertain threat environment.
Frequently Asked Questions
What is proactive web anomaly monitoring and how does it differ from traditional security?
Proactive web anomaly monitoring continuously analyzes web traffic and system behavior in real time, detecting threats as they emerge rather than discovering them weeks or months later. Unlike traditional security approaches that rely on periodic scans and signature-based detection, proactive monitoring uses behavioral analysis to identify unusual activity patterns that indicate potential attacks. This approach catches zero-day exploits and novel attack methods that signature-based systems miss, while dramatically reducing the time between attack initiation and detection.
How quickly can automated website file integrity monitoring detect unauthorized changes?
Automated website file integrity monitoring detects unauthorized file changes within seconds to minutes of occurrence. The system continuously compares current file states against baseline cryptographic hashes, immediately flagging any modifications. This rapid detection enables your security team to respond before compromised files cause significant damage, often containing incidents within the critical 15-minute window that prevents minor breaches from escalating into major crises.
What makes brute force login protection effective against credential-based attacks?
Effective brute force login protection analyzes login attempt patterns rather than simply counting failed logins from individual IP addresses. The system recognizes distributed attacks spread across multiple sources, identifies credential stuffing attempts using breached password databases, and detects anomalous login behaviors like access from unusual locations. This comprehensive approach blocks sophisticated attacks that evade basic rate limiting, while graduated response measures prevent legitimate users from being locked out due to forgotten passwords.
Can mid-market firms afford enterprise-grade website security incident response capabilities?
Yes, modern proactive web anomaly monitoring systems make enterprise-grade security accessible to mid-market organizations through automation and cloud-based deployment models. These systems require minimal additional staffing because automated detection and initial response handle routine security tasks. Cloud deployment eliminates large upfront infrastructure investments, while managed service options supplement internal teams with specialized expertise. The cost of these capabilities is substantially lower than the average cost of a single data breach, making them a sound financial investment for organizations of all sizes.
How does web threat mitigation support business continuity and growth?
Web threat mitigation protects the digital infrastructure that modern businesses depend on for operations, customer engagement, and revenue generation. By preventing successful attacks and containing incidents quickly when they occur, these capabilities ensure that your web properties remain available and trustworthy. This operational stability enables you to pursue digital transformation initiatives, expand online services, and enter new markets with confidence that security infrastructure will protect these growth activities rather than constraining them.
How Elevated Marketing can help
We do this work every day for businesses in Indianapolis, the DC & Virginia metro, and nationwide.
→ Website Security & Monitoring→ SEO & GEO Services→ Managed Web Hosting→ More on UncategorizedGet a free audit